U.S. investigators also warned that the attackers secretly record the video calls and use that material to prepare new scams. In this way, they can replay conversations and familiar faces to deceive others, multiplying the reach of the campaign.
The FBI assured that the communist regime in North Korea uses these operations to finance its weapons program
The FBI's cybersecurity director, Brett Leatherman, noted that the North Korean regime relies on the income obtained through massive cryptocurrency thefts to finance its illegal weapons program. According to the official, Pyongyang has stolen billions of dollars in digital assets over the past few years.
The FBI described ''FaceStealer'' as a highly effective social engineering operation, capable of deceiving even users with technical experience and advanced cybersecurity knowledge.
Patrick Grandy, deputy director in charge of the FBI office in Los Angeles, explained that the method exploits people's trust in video conferencing platforms and their personal relationships.
The alert came just a week after Binance, the world's largest cryptocurrency exchange, revealed that hackers had used fake job interviews to perpetrate a record theft of 6.3 billion dollars. U.S. agencies attributed that attack to actors linked to North Korea, although Pyongyang denied its involvement.
The succession of incidents reinforces Washington's warnings about the use of cyber operations by the North Korean regime to obtain financial resources outside traditional channels. Authorities continue to investigate the activities of ''FaceStealer'' and warn about the need to carefully verify the identity of participants in virtual meetings, especially when they request to install programs or access external links.
Recently, agents associated with the Kim Jong Un regime launched a massive attack on the crypto asset platform, Binance
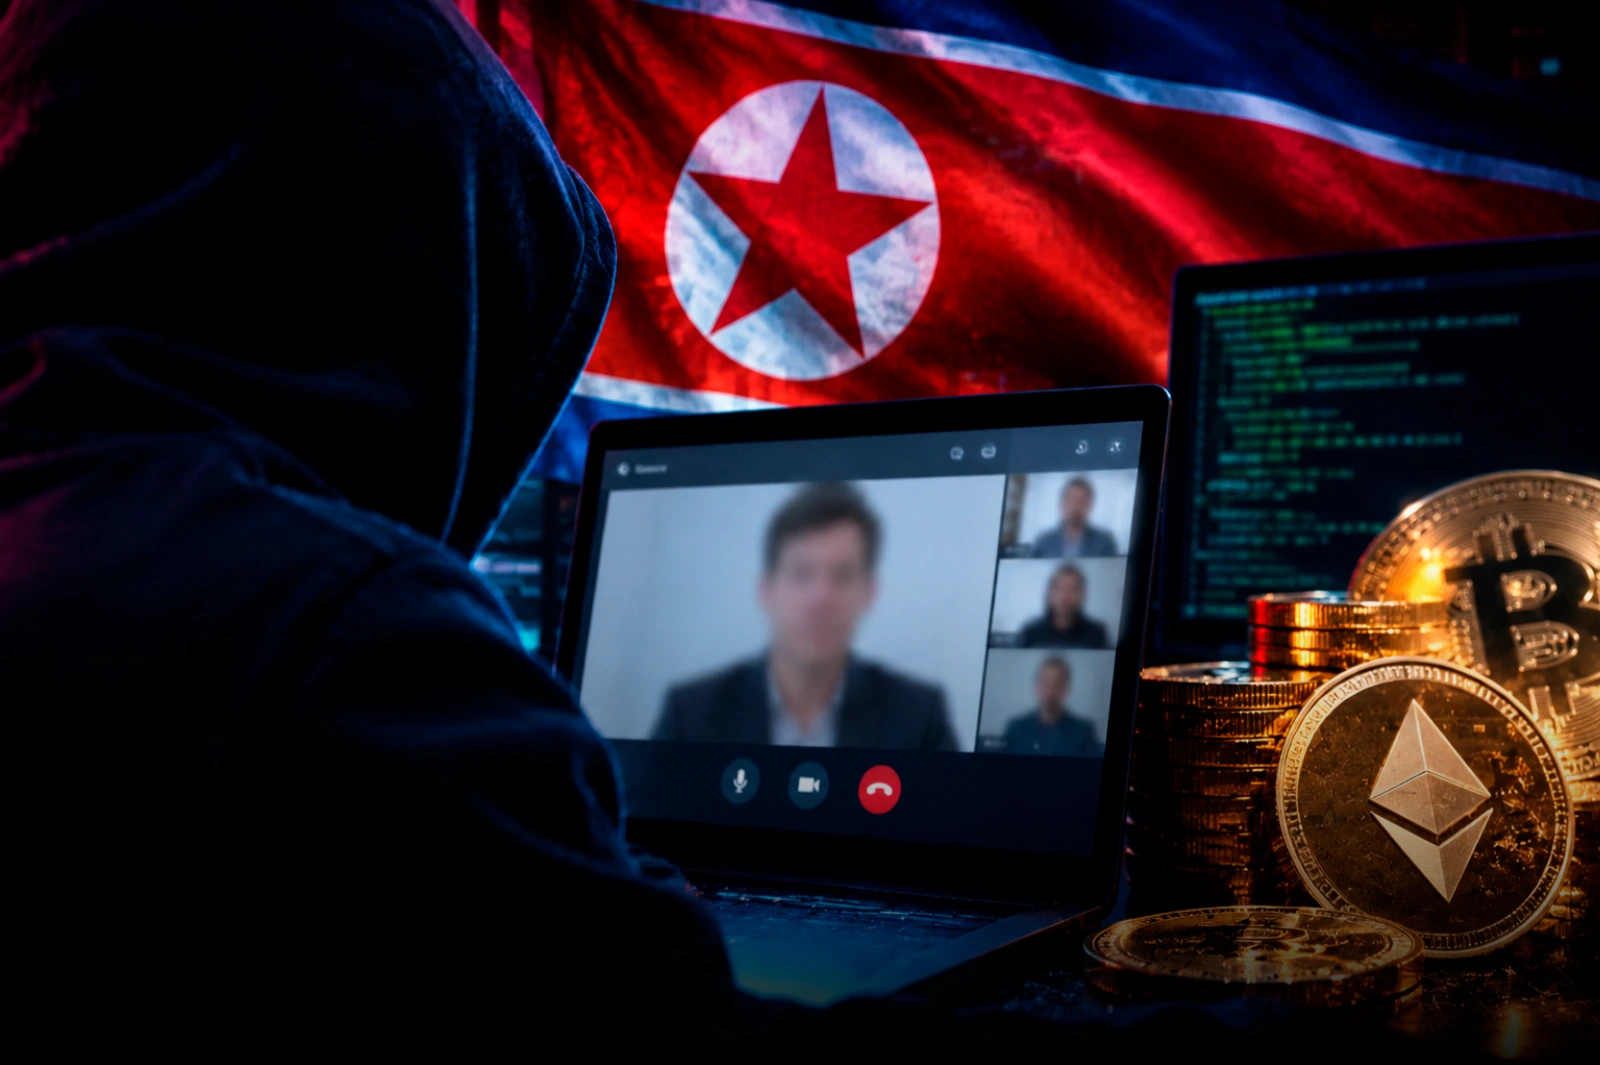
Hackers linked to the regime of North Koreastole more than 400 million dollars in cryptocurrencies through a sophisticated identity theft campaign that uses fake video calls to infect devices and access confidential information. The FBI identified the operation as ''FaceStealer'' and warned that more than 900 people have fallen victim to the scheme over the past 18 months.
The investigation by U.S. authorities indicates that the attackers use fake or hijacked social media accounts to contact potential victims and invite them to participate in virtual meetings. The campaign particularly targets workers in the cryptocurrency and ''Web3'' sectors, including developers and specialists responsible for maintaining open-source programs.
According to the FBI and the U.S. Department of Justice, the criminals organize video calls using fraudulent versions of widely used platforms, such as Zoom, Microsoft Teams, and Google Meet. In this way, they seek to build trust and make their targets believe they are participating in a legitimate meeting with acquaintances or professional contacts.
A North Korea-related hacking group stole more than $400 million in cryptocurrency
During the calls, the attackers play previously recorded videos of other victims that the contacted person recognizes. The goal is to simulate an authentic conversation, although a supposed technical problem with the audio later appears.
At that moment, a notification on the screen asks the user to resolve the issue by clicking on a link. However, the supposed repair mechanism installs malicious software on the device.
Once executed, the malware allows hackers to access the contact lists and various applications on the compromised device. This provides them with information to expand the operation and select new targets, leveraging the personal and professional relationships of the initial victims.